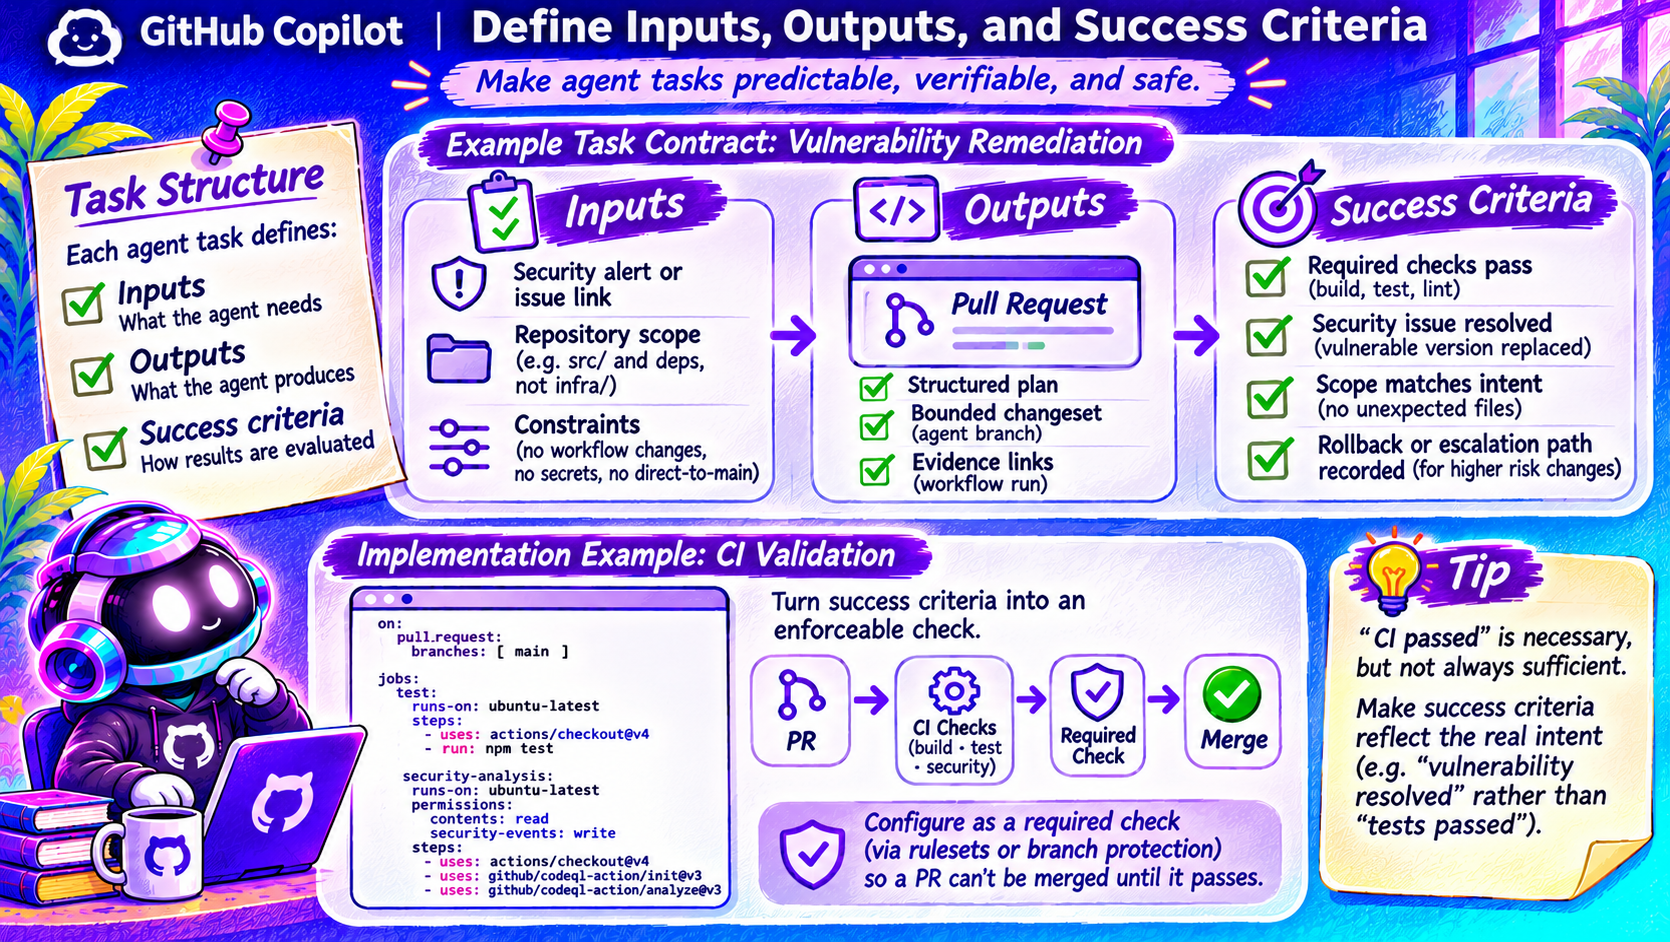
Define a task contract
Specify inputs, outputs and success criteria so an agent's work can be evaluated against the real goal.
Inputs: what the agent needs
The image's vulnerability-remediation example starts with an alert or issue, the permitted repository scope and constraints. State which files may change, what must remain untouched and what information is missing.
Outputs: what the agent must produce
A useful result includes a bounded changeset, a structured explanation and links to validation evidence. For higher-risk work, include rollback or escalation information. Do not accept a generic success statement in place of inspectable artifacts.
Success criteria: how the result is judged
Required checks passing is necessary in many workflows, but it may not prove the actual goal. Confirm that the vulnerable version was replaced, the scope stayed within bounds and the intended behavior is covered.
Turn objective criteria into required checks where possible. Keep human decisions explicit. The YAML screenshot is illustrative and should not be copied as a complete, secure workflow.
Before starting, ask whether an independent reviewer could decide success using the contract and the resulting evidence.