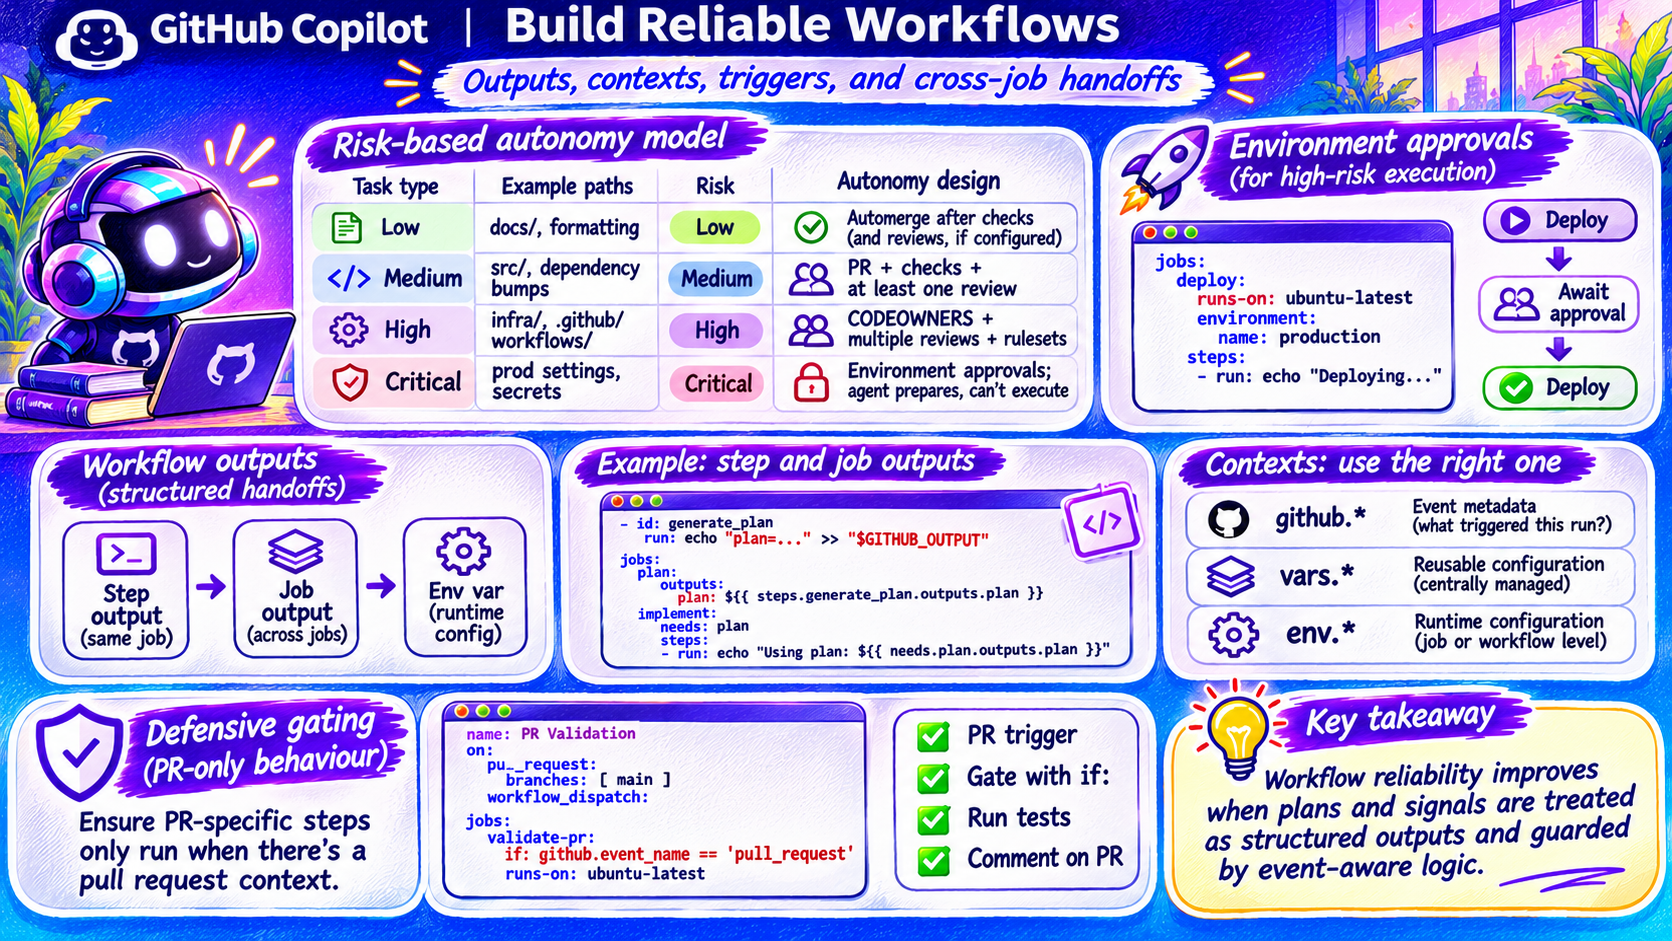
Build reliable workflow handoffs
Carry structured outputs between jobs, use the right context and gate execution according to event and risk.
Treat handoffs as data
The image distinguishes step outputs, job outputs and runtime environment variables. A value needed in another job must be deliberately exported and passed through the workflow's supported output mechanism. Do not assume shell state persists between jobs.
Use context intentionally
Event metadata, configured variables and runtime environment values serve different purposes. Check whether a workflow has a pull-request context before performing pull-request-specific actions. Manual runs and other triggers may lack that data.
Treat event fields and generated output as untrusted input. Avoid interpolating them directly into executable shell commands.
Apply risk-sensitive execution
The image progresses from low-risk documentation work to sensitive infrastructure and production operations. This is an example policy framework, not a default GitHub behavior or a recommendation to auto-merge every documentation change.
Use narrowly scoped job permissions, protected environments where appropriate and explicit approval for high-impact operations. Validate actual event paths and failure cases rather than only testing the happy path. Pictured YAML fragments are not complete workflows.